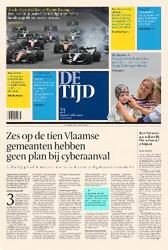
ACEN is featured once again in De Tijd, one of Belgium’s leading business newspapers.
In an article on the cybersecurity of Flemish local authorities, Wouter Decruy, Managing Director at ACEN, comments on a striking report by Audit Vlaanderen: six in ten municipalities tested have no plan to keep their services running after a cyberattack.
Key insights from the article
- No authority without weak spots
Auditors found 1,899 vulnerabilities across 77 Flemish municipalities and 12 intermunicipal companies, 353 of them high-risk. - Continuity plans are missing
59 percent of local authorities and 67 percent of intermunicipal companies could not produce a business continuity plan. - AI exposes old flaws faster
Many organisations run older software whose flaws AI can detect faster and more thoroughly. Defences are lagging behind, and the lists of shortcomings keep growing. - Practice is essential
As with a fire drill, only by practising do you find out whether your arrangements really work. A plan also has to keep pace with your applications, suppliers and processes. - Security requires choices
Protection takes expertise and investment. Local authorities have to choose carefully where to focus their budget.
Six in ten Flemish municipalities tested have no plan for a cyberattack
Auditors have found hundreds of serious security problems at dozens of Flemish cities and municipalities. Six in ten of the local authorities examined also cannot produce a plan to keep their services running after a cyber incident.
During security checks of the IT systems of Flemish local authorities, auditors found no fewer than 1,899 digital vulnerabilities, 353 of them high-risk. That is the finding of a new report by Audit Vlaanderen, which brings together local ICT security audits from 2023 to 2025. During that period, 77 of Flanders’ roughly 300 municipalities and 12 intermunicipal companies took part in the programme. Not a single authority examined was free of weak spots.
“During security checks of Flemish local authorities, auditors found 1,899 digital vulnerabilities, 353 of them high-risk.”
The poor preparation for IT system outages stands out in particular. Of the local authorities examined, 59 percent had no business continuity plan. Among the intermunicipal companies, the figure was 67 percent. Such a plan should set out how an organisation keeps essential services running and restores its systems when the computers go down. The auditors only checked whether authorities could produce a plan; its content was not even assessed.
How quickly a software flaw can disrupt services became clear once again on Wednesday, after warnings about vulnerabilities in the widely used programming language PHP. Numerous Flemish, federal and foreign government services took their websites offline as a precaution, as did many private companies.
Insecure passwords also remain a weak spot. On average, 30 percent of the passwords tested at local authorities are weak. For administrator accounts, which can often give access to an authority’s entire ICT environment, the average was 18 percent.
“30 percent of the passwords tested are weak. The same goes for 18 percent of system administrators’ passwords.”
In a response, the Association of Flemish Cities and Municipalities (VVSG) stresses that many local authorities are catching up significantly on cybersecurity. According to the VVSG, stricter European security requirements play an important role in this.
The authorities that took part voluntarily are not a representative sample of all Flemish cities and municipalities. Audit Vlaanderen nevertheless states that the findings are in line with earlier studies.
It is not known how many of the identified shortcomings have since been resolved. The participating authorities received their findings and had to act on them themselves.
Ever longer lists
The rise of artificial intelligence has fundamentally changed cybersecurity for local authorities too, experts say. “Attackers can use AI to find flaws in software faster,” says Lauren Cuyvers, partner in the Privacy and Cybersecurity Practice of law firm Crowell & Moring. “At the same time, defenders can use the same technology to find and close those gaps.”
“Protection requires expertise and investment. These are not small or cheap projects. Local authorities have to make budget choices about where to focus.” – Wouter Decruy (Managing Director at ACEN)
Many organisations are currently in a transitional phase, says Wouter Decruy of cybersecurity company ACEN. They use older software with security flaws that have so far gone unnoticed, but that AI can detect faster and more thoroughly. Defences against this, however, are lagging behind.
Only with the next generation of software will developers be able to use the same technology before launch to find and fix flaws. Decruy therefore expects new versions to contain fewer vulnerabilities over time. In the meantime, organisations have to close the exposed gaps in their existing software.
That involves a lot of work. ACEN secures, among others, government organisations, cities and municipalities. “Clients install security updates, but at the next check they still get another long list of shortcomings,” says Decruy. “And those reports are only getting bigger.”
Digital fire drill
The pressure to close identified software flaws can push other preparatory work, such as a continuity plan, into the background. Such a plan should make clear what happens when systems go down. How are citizens and staff informed? And in what order can applications be safely restarted? A cyberattack on the city of Antwerp at the end of 2022 was still having major consequences for its services months later.
Decruy compares the preparation to fire drills: only by practising do you find out whether the arrangements really work. The plan also has to be updated whenever applications, suppliers or work processes change. Cuyvers likewise advocates simulations in which staff and managers have to respond in real time.
Moreover, the risks do not lie solely within the organisation itself. Software suppliers sometimes get far-reaching access to systems. “Organisations must therefore clearly agree who is internally responsible for what, backed by watertight contracts with that supplier,” says Cuyvers.
Such protection requires expertise and investment. “These are not small or cheap projects,” says Decruy. “Local authorities have to choose where to focus their budget.”
Manon Brasseur – De Tijd