NIS2
Compliance

NIS2 obliges thousands of Belgian organisations to demonstrably get their cyber resilience in order, with personal accountability for the board.

We translate that legal obligation into a concrete, feasible journey.

From scoping and registration with the CCB, through a gap analysis against the CyberFundamentals framework, to a roadmap towards conformity and the preparation for verification. Pragmatic and at the pace of your organisation.

Common problems
Our solutions

You are not sure whether and how NIS2 applies to your organisation.

The criteria for sector, size and role in the supply chain are complex. Without a clear answer, you risk missing obligations or putting effort where it isn’t needed.

Our scoping check determines whether you are an Essential or Important entity.

What that means for supervision and sanctions, and which registration obligations with the CCB apply.

Translating the legal text into concrete measures is a blind spot.

The law says what you need to achieve, not how to achieve it. Teams end up with a long list of requirements and no clear idea where to begin.

In Belgium, CyberFundamentals is the practical benchmark for NIS2.

We perform a gap analysis against the right assurance level (Basic, Important or Essential) and translate every gap into a concrete, prioritised action.

The board is personally accountable but has no view of the status.

Directors can be held liable, yet they get scattered updates or none at all. Without a clear picture, they can’t steer or show that they are fulfilling their duties.

We bring governance and reporting to board level.

Clear maturity scores, a ten-point roadmap and a reporting rhythm with which the board demonstrably fulfils its duty of care.


Results

What can you expect?

Scoping & registration advice

Clarity on your NIS2 status (Essential or Important), the corresponding obligations and the registration with the CCB.

Gap analysis against CyFun

A scored comparison with the right assurance level, following the same methodology as the official verification.

Roadmap & policy set

A prioritised plan towards conformity with effort, budget and timeline, complemented by a recommended set of policy documents.

Preparation for verification

Guidance towards CyFun verification or certification, the presumption of conformity that strengthens your position with the regulator.

Some ACEN members of varying rteams seated in a meeting room with their backs turned towards us.
BLog article

Dutch Cybersecurity Act: Insights from Belgium’s NIS2 journey

Some ACEN members of varying rteams seated in a meeting room with their backs turned towards us.

The Cybersecurity Act (Cbw) has been in force since 15 August 2026. It turns the European NIS2 Directive into Dutch national law, and it is changing the Dutch cybersecurity landscape at its core.

Thousands of organisations are now legally required to systematically strengthen their cyber resilience. The government’s message is clear: the time to wait is over.

How we approach a NIS2 journey

Phase 1 Scoping & registration

We determine your status under the Belgian NIS2 law, the corresponding obligations and deadlines, and guide the registration with the Centre for Cybersecurity Belgium. Immediate clarity on incident notification, supervision and sanctions.

Phase 2 Gap assessment

Through workshops with your stakeholders we measure the organisation against the appropriate CyFun assurance level. We follow the Conformity Assessment Schema, so the result is directly usable on the road to verification.

Phase 3 Roadmap & policies

Every gap becomes an action with priority, effort and budget indication, bundled in a roadmap built around ten key points. We deliver a recommended policy set and guide the rollout at the pace of your organisation.

Phase 4 Verification & continuity

We prepare you for the CyFun verification and anchor an annual rhythm of measurement and adjustment. With an awareness programme and periodic AI-driven pentests you also make the resilience demonstrable in practice.

A successful CyberFundamentals verification provides a presumption of conformity with NIS2 in Belgium. We build the entire journey along that benchmark, so every step pays off twice.

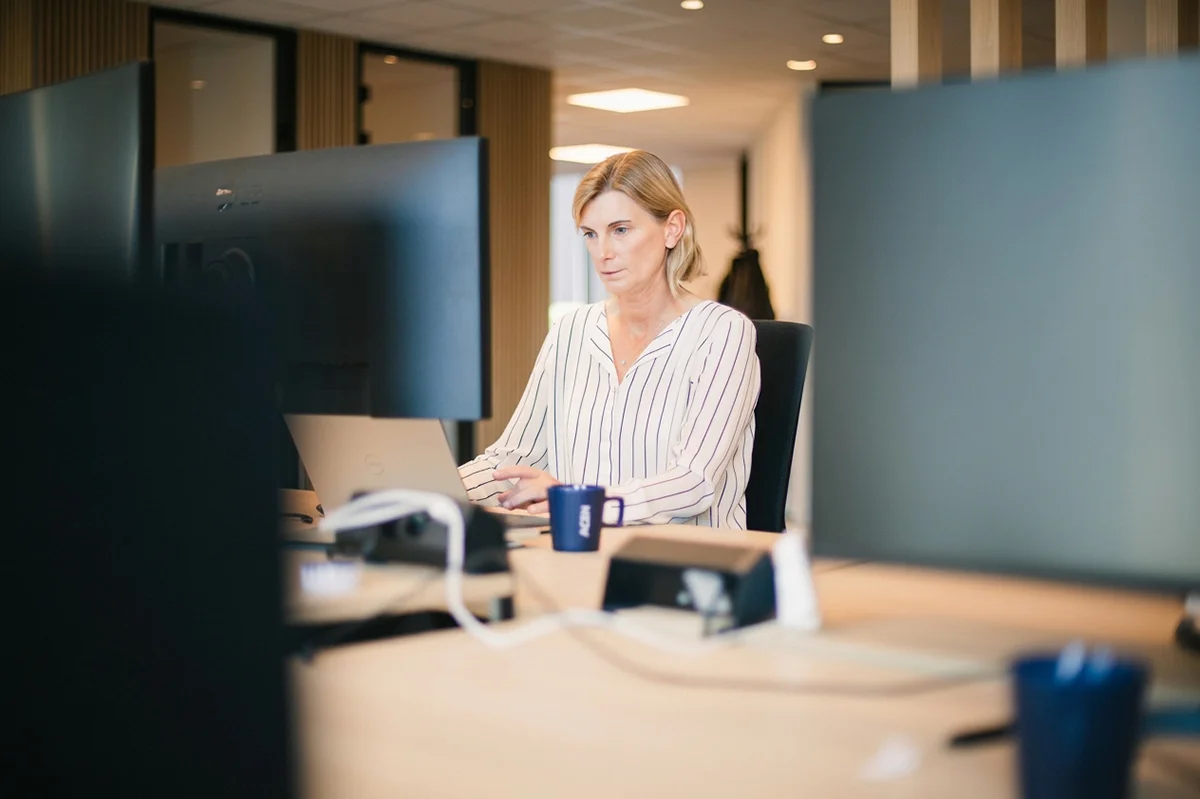
A female member of the Advisory team smiling behind a pc in the Kontich office.

Do you still have some questions?

Contact

Your road to NIS2 starts here.

FAQ

Everything you still wanted to know in one place

How long does a NIS2 journey to conformity take?

The gap analysis runs a few weeks. The remediation journey depends on your starting point and ambition level and typically runs over several quarters, divided into manageable steps.

We are ISO 27001 certified. Is that enough?

ISO 27001 is a strong foundation but does not fully cover NIS2. We map your existing certification onto the NIS2 requirements and only fill the remaining gaps, without duplicating work.

What does NIS2 call for in case of an incident?

NIS2 imposes a staged notification duty: an early warning within 24 hours, an incident notification within 72 hours and a final report.

We help you set up those notification processes in advance so you never improvise against the clock.

What is CyberFundamentals and why do you use it?

CyFun is the framework of the Centre for Cybersecurity Belgium and the practical benchmark for NIS2 in Belgium. A successful verification provides a presumption of conformity, so every effort counts twice.

What is the difference between a NIS2 Essential and an Important entity?

Essential entities fall under proactive supervision and the heaviest sanctions. Important entities are supervised ex post, after an incident or indication. The measures are similar, the supervision regime differs.

Does my organisation fall under NIS2?

That depends on your sector, your size and your role in the supply chain. Our scoping check quickly provides certainty, also for edge cases such as suppliers of essential entities.

Explore our other Cyber Security Advisory Services

Awareness Program

AI-driven Exposure Management

Maturity Assessment

ACEN logo with orange swirl
Privacy Overview

This website uses cookies so that we can provide you with the best user experience possible. Cookie information is stored in your browser and performs functions such as recognising you when you return to our website and helping our team to understand which sections of the website you find most interesting and useful.