Cyber Security Advisory Services

Did you know?

60%* of data breaches involve a human element: a phishing click, a stolen password or a simple mistake. Technology alone can’t close that gap.

*Ref: Verizon DBIR 2025

WHY

Why is this service important?

How well is your organization protected? Answering that question is harder than asking it. You are balancing daily operations and limited budgets against evolving threats and stricter regulation such as NIS2. Meanwhile your board, your insurer and your customers are asking for proof that your cyber resilience is in order.

ACEN Advisory brings structure to that challenge. We guide organisations along a clear growth path: we make your people resilient, we map your organisation objectively and we prove with a real test that your defences hold. Pragmatic, vendor-neutral and anchored in the official Belgian CyberFundamentals framework.

From compliant on paper to demonstrably resilient in practice.

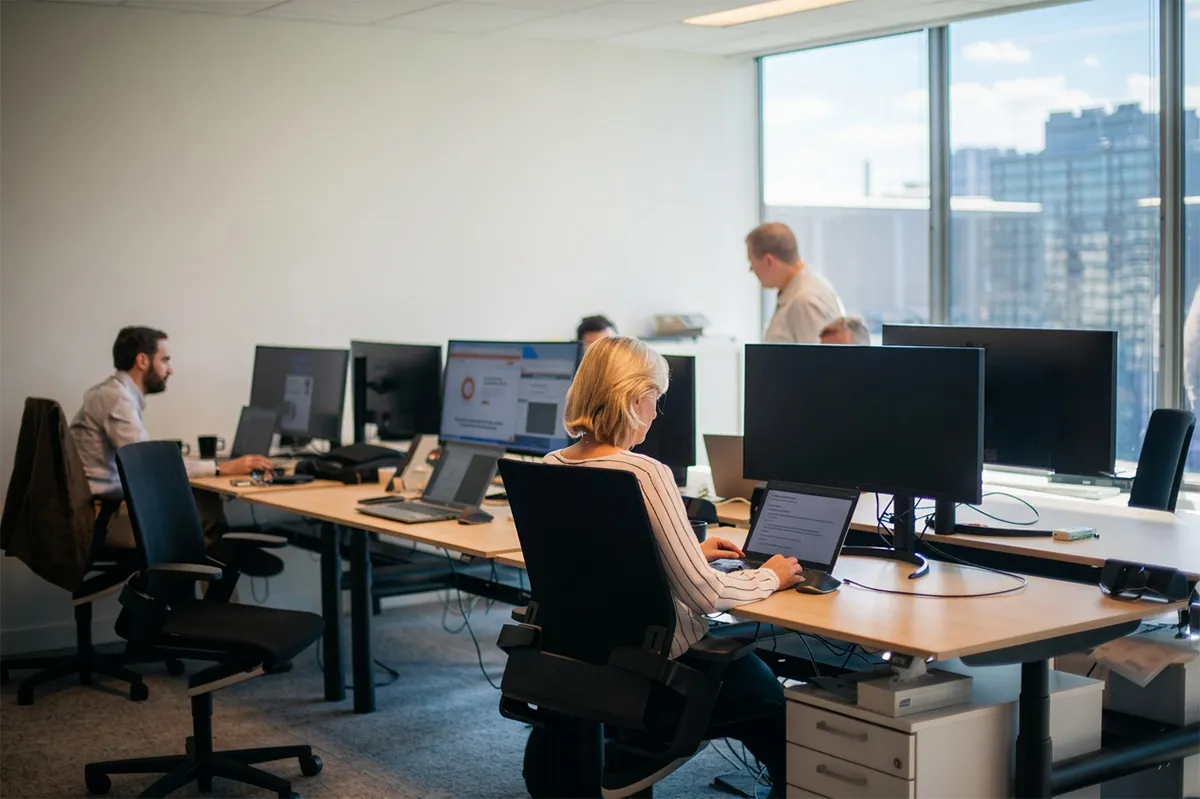
Image of the ACEN office with some members of the Advisory team grouped together at their desks.

Do you recognise these pain points?

No objective view of where you stand today
NIS2 obligations without a clear starting point
Employees remain the most exploited attack vector
No proof that your defences stop a real attack
Subservices

Discover our Cyber Security Advisory services

NIS2 Compliance

NIS2 holds thousands of Belgian organisations, and their boards, accountable for demonstrable cyber resilience. We turn that obligation into a concrete journey: scoping and CCB registration, a CyberFundamentals gap analysis, a roadmap to conformity and preparation for verification. It’s pragmatic and moves at your pace.

Awareness Program

People remain the most exploited attack vector, and no technical control fixes that. Our awareness programme reduces human risk through a continuous cycle of phishing simulations, interactive training and live hacking demos. One subscription, measurably safer behaviour.

AI-driven Exposure Management

An assessment shows a control exists, not that it stops a real attacker. Our AI-driven pentesting autonomously tests your Active Directory, network and Microsoft 365. Results come in days, not weeks, can be repeated anytime, and make improvement visible instead of assumed.

Maturity Assessment

How mature is your cybersecurity, really? In workshops with your stakeholders, we score your people, processes and technology against Belgium’s official CyberFundamentals framework. You get a clear, prioritised action plan: a practical starting point, not a theoretical audit.

APPROACH

How we offer Cyber Security Advisory

Every organisation enters where it stands today. The three steps reinforce each other and form one journey.

Awareness: make your people resilient

People remain the most exploited attack vector, and no technical control fixes that. With a continuous awareness programme we build measurably safer behaviour, from phishing simulations to live hacking workshops. Low threshold, immediately visible results and no prior maturity required.

Insight: map your organisation

A maturity assessment translates an abstract obligation or ambition into a concrete, scored view of where you stand. Anchored in the CyberFundamentals framework of the Centre for Cybersecurity Belgium, with a prioritised roadmap as the result. For organisations with a NIS2 obligation we guide the full compliance journey.

Proof: test whether your defences hold

An assessment shows that a control exists. It does not prove that it stops a real attacker. With AI-driven pentesting we validate your full internal attack surface in days instead of weeks, at a fraction of the price of a classic pentest and repeatable at any moment.

CyFun logo; CCB shield graphic with in text CyFun next to it.
CCB CyberFundamentals
OutKept logo
OutKept

With these partners

Reference cases

Explore previous service projects

AI-driven Exposure Management. AI-gedreven exposure management. Photo of the ACEN Advisory team during a meeting.

Continuous Threat Exposure Management: Which security issues matter most?

OutKept banner for website

Phishing prevention is key for cyber resilience: ACEN and OutKept join forces

OutKept banner, campaign image for phishing awareness with a fisherman holding a fish.

ACEN partners with OutKept to transform phishing awareness training

contact

Get in touch with our experts

FAQ

Everything you still wanted to know in one place

Can the advisory findings support discussions with our board, customers or cyber insurer?

Yes. Reports and executive summaries can help explain your current position, the actions taken and the remaining risks.

We discuss who the information is intended for and which findings can be shared. Specific requirements from a customer or insurer should be checked upfront, so the engagement can take them into account.

A report does not automatically replace their own assessment or approval process.

What happens after the assessment, training programme or pentest is completed during advisory projects?

We review the results with you and agree the next steps. Your team can use the recommendations to make improvements, with further support where needed.

After a pentest, a retest can validate the fixes. The awareness programme closes its annual cycle with a review and proposed priorities for the following year. The follow-up depends on your goals and the scope we agree.

How do you help management turn cybersecurity findings into investment priorities in advisory projects?

We connect the findings to their potential business impact and explain them in language management can use. Depending on the engagement, the roadmap includes priorities, effort estimates and budget indications.

That gives you a basis for deciding what to address first, what can wait and who should take ownership.

How does advisory differ from an audit, a pentest or a managed security service?

Advisory helps you understand risks and turn them into a practical plan. An audit checks conformity against a defined standard. A pentest tests what an attacker can achieve within an agreed technical scope.

Managed security services provide ongoing operational support, such as monitoring and response. These services can complement each other. We help you decide which combination fits your needs.

Can ACEN advisory work with our existing IT partner, security tools and internal team?

Yes. We start by understanding what is already in place and who is responsible for it.

Your internal team and IT partner bring valuable knowledge of the environment. We build on that, identify gaps and agree who will handle the next steps. Our advice is vendor-neutral, with recommendations based on your risks and priorities.

What determines the cost of an advisory engagement, and how do we get started?

The cost depends on the service, the scope of your organisation and environment, and the level of support you need. Some services are project-based, while the awareness programme follows an annual subscription model. Start with an introductory conversation about your situation and goals.

We then propose a scope, expected deliverables and price, so you know what you are committing to before the work begins.

How much time and involvement will you need from our advisory team?

We agree this with you before starting. An assessment needs input from the people who understand your systems, processes and business priorities. An awareness programme needs coordination and time for training and review sessions. A pentest needs technical scoping and follow-up on the findings.

We make those expectations clear upfront so you can plan the work alongside your daily operations.

What concrete results will we receive, and how do you measure progress?

The results depend on the service and scope you choose. A maturity assessment gives you a scored view of your organisation and recommendations, with roadmap detail depending on the selected level. An awareness programme tracks behaviour such as clicking and reporting phishing emails. Exposure management gives you validated attack paths and remediation advice. Follow-up measurements and retests help show what has improved and what still needs attention.

Is Cyber Security Advisory relevant if we do not fall under NIS2?

Yes. Protecting your operations, data and customer relationships matters whatever your regulatory status. You may also need a clearer view of your risks for management, customers or your cyber insurer.

Advisory helps you identify practical improvements and use your available budget where it makes the most difference. NIS2 can be a reason to start, but it is not the only one.

Can we start with one advisory service, or do we need the full advisory journey?

You can start with one service. Each addresses a specific need, and the next step depends on what your organization needs and can realistically take on. An assessment might lead to an awareness programme or a pentest, for example.

We agree the scope with you first and use the findings to decide whether further support would be useful.

Which advisory service is the right starting point for us?

That depends on the question you need to answer. If you lack an overview of your risks, a maturity assessment is a good place to start. If phishing and employee behaviour are your main concern, look at our awareness programme. AI-driven exposure management helps validate your technical defences. If NIS2 is the immediate driver, we help you understand your scope and plan the journey.

We can work out the right starting point together in an introductory conversation.

What does Cyber Security Advisory help my organization achieve?

We help you understand where your organisation stands today and decide what to improve first. Depending on your needs, that can mean building safer behaviour among employees, assessing your cybersecurity maturity or testing whether your defences hold up in practice.

You get clear findings and practical next steps that your IT team and management can work with.

ACEN logo with orange swirl
Privacy Overview

This website uses cookies so that we can provide you with the best user experience possible. Cookie information is stored in your browser and performs functions such as recognising you when you return to our website and helping our team to understand which sections of the website you find most interesting and useful.