Detection and Response Services

Did you know?

In 4 out of 5* security incidents, the warning signs were there. But was there anyone looking for them?

*ref: Osterman Research

Why

Do you need these services?

Traditional security measures alone are no longer enough to stop today’s cyber threats. Firewalls and antivirus keep the obvious out, but modern attackers log in with stolen credentials, move quietly through your network and use AI to strike at machine speed. Meanwhile, many organisations lack the people, time and specialist knowledge to keep watch around the clock.

The question is no longer if an attacker gets in, but how fast you spot them and how decisively you act.

ACEN brings detection and response together in one approach. We map what’s exposed, fix what’s vulnerable, monitor your environment 24/7 from our local SOC (Security Operations Center), and step in the moment something happens.  That way threats are contained within minutes, not days.

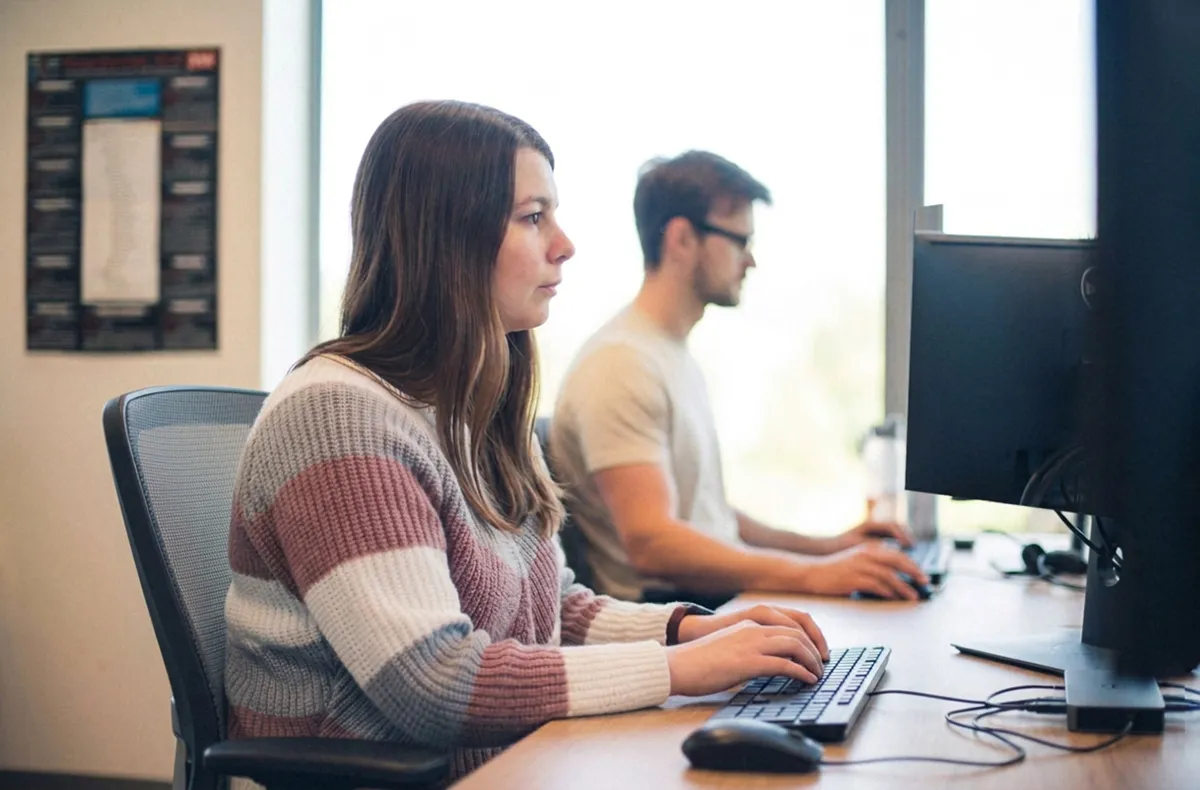
Detection and Response. Image of two ACEN employees of the MDR team at work in the Security Operations Center.

Do you recognise these pain points?

Internal IT constraints make 24/7 continuous monitoring impossible
Not enough internal resources or expertise to handle an incident or breach
Alert fatigue causes critical threats to go unnoticed
Dedicated security experts are hard to find
Subservices

Discover our Detection and Response services

Vulnerability Management

External Attack Surface Management continuously discovers and inventories everything visible to an outside attacker. That includes public domains and subdomains, exposed cloud services, internet-facing applications, and forgotten or unmanaged assets. Shadow IT is covered too.

Incident Response and Forensics

Think you’ve been breached? Our Incident Response & Forensics team investigates, contains, and helps you recover from cybersecurity incidents, from phishing and ransomware to full scale data breaches.

Managed Detection and Response (MDR)

Get the support and decisiveness of a fully operational, local Security Operations Center (SOC). Our experts monitor, detect and respond to threats across your entire IT environment 24/7, acting as a true extension of your in-house team.

External Attack Surface Management

You can’t protect what you don’t know exists. We continuously discover everything an attacker can see from the outside: domains, cloud services, internet-facing applications and forgotten assets. That way you know what’s exposed before they do.

Approach

Our proven Detection & Response successes

Response-Centric

Relieve customers by managing their security operations. Breaches are flagged and contained within minutes, not days, through a single point of contact, clear ownership, and pre-agreed SLA response times.

Synergy of AI & human

AI ranks exposures by business impact and real-world exploitability, not raw severity scores. Our experts review every finding before it's acted on, so priority reflects what threatens you.

Focus On Identity

Focus on identities, the way in behind most breaches, 83% of which involve compromised credentials, to scope defense around how attackers actually get in, not just what's easiest to monitor.

Continuously Validated

Validate continuously, not once a year. Real attack paths are tested safely against live environments, and every fix is re-verified afterward, so exposure closes for good instead of just on paper.

Horizon3.AI logo, Brain graphic in white and red with in grey 'HORIZON', spelled next to it.
Horizon3.AI
logo munitio
Munitio
Google Security Operations Logo
Google Security Operations
vectra-ai logo
Vectra
SentinelOne logo
SentinelOne
Tenable logo
Tenable
Silverfort logo
Silverfort

With these partners

Reference cases

Explore previous service projects

Reference case banner Willemen Groep met logo

A solid security foundation for 100 construction sites

Reference case banner A&C

A strategic alliance in cybersecurity between A&C systems & ACEN MDR

Copy of Acen - website overview image - 1500 x 1000px (10)

UZ Leuven counts on Nynox to protect sensitive patient data

contact

Get in touch with our experts

FAQ

Everything you still wanted to know in one place

Does 24/7 mean I can reach ACEN MDR anytime? And how do I?

You'll have a dedicated single point of contact for all communication and reporting.  Depending on the agreed SLA, our experts can respond in as little as one hour.

Can this managed service replace our need for internal security staff?

Our SOC works as an extension of your internal IT team. We bring expertise, experience, and capacity to strengthen your security operations.  Depending on contract details and agreed policies, our analysts operate as part of your team.

This helps to close knowledge and resource gaps and can eliminate the need to have your own security team.

How quickly can MDR be assessed and deployed?

We always start with a thorough assessment to understand your as-is situation. Regarding business and security needs, we design a plan that works for you.

Initial research typically takes about 6-8 weeks. Deployment happens within 48 hours, providing you with a monitoring baseline quickly.

How many incidents do you handle annually?

Our team handles more than 500 alerts a month and responds to over 200 incidents and breaches each year.  Cyber incidents are inevitable. It's important to have a plan and be prepared for when it happens.

ACEN logo with orange swirl
Privacy Overview

This website uses cookies so that we can provide you with the best user experience possible. Cookie information is stored in your browser and performs functions such as recognising you when you return to our website and helping our team to understand which sections of the website you find most interesting and useful.