Maturity
Assessment

How would you rate your cybersecurity environment? Our maturity assessment answers that question objectively and measurably.

In collaborative workshops with your stakeholders we map people, processes and technology, score your maturity against the official Belgian CyberFundamentals framework (CCB) and translate the findings into a concrete, prioritised action plan. Not a theoretical audit but a practical starting point, available in three levels: Core, Foundation and Advanced.

Common problems
Our solutions

You have no objective view of where your organisation stands today.

Security decisions are based on gut feeling or whoever raises the loudest concern. Without a clear baseline, it’s hard to justify budget or know where to start.

The assessment scores your maturity systematically against CyberFundamentals, with clear visuals per domain.

You know exactly what is strong, what is missing and what deserves priority.

Reports full of recommendations paralyse instead of activate.

A thick report with dozens of findings lands on the desk and stays there. Nobody knows what to tackle first, so nothing moves.

We deliver a roadmap built around ten key points

Each with actions, an effort estimate, a budget indication and a timeline. A plan your organisation can execute itself and report on to management and steering committees.

Classic audits feel like an exam and end in a checklist without context.

Teams feel judged rather than helped, so they give the expected answers instead of the real ones. The result shows what’s on paper, not what happens day to day.

Our assessment is collaborative and pragmatic.

We test how policies and controls really live in daily operations, and our advice is honest, independent and vendor-neutral.


Results

What can you expect?

Strategic maturity report

Findings, maturity scores and in-depth analysis, with concrete recommendations for your technical teams.

Executive presentation

The core results and the way forward, distilled for leadership and stakeholders, styled in your branding.

Prioritised roadmap

Ten key points with effort, budget indication and timeline (bundled with Foundation, included in Advanced).

Wrap-up with your team

Presentation of the results to the IT team and stakeholders, with clear next steps.

NIS2 hero image
BLog article

Who is responsible when things really go wrong?

NIS2 hero image

We, at ACEN, love to think about cybersecurity as a car (your business) navigating and driving through the digital world.

Just like any car trip, ensuring a smooth and pleasant ride requires a few things. So to enforce a strong cybersecurity strategy and posture we rely on the CyberFundamentals Framework, created by the CCB.

How we approach an assessment

Phase 1 Discovery & scoping

We start with interviews and a document review, and determine the right target profile for your organisation through a threat modeling exercise (based on the CCB CyFun Selection tool). This way the assessment measures against a realistic ambition level.

Phase 2 Maturity workshops

In collaborative workshops with your key stakeholders we review policies, standards and controls, and above all how they are woven into daily operations. That way the findings reflect reality, not the paper version.

Phase 3 Analysis & reporting

Our experts analyse the findings, score your maturity against the chosen framework and identify strengths and weaknesses. We apply the same approach as auditing parties (the CyFun Conformity Assessment Schema), so you know exactly where you stand on the road to verification.

Phase 4 Roadmap & prioritisation

We translate everything into a tangible report with a prioritised roadmap. In dialogue with management we determine what is realistic and feasible within your budget, focusing on the steps that drastically increase your resilience.

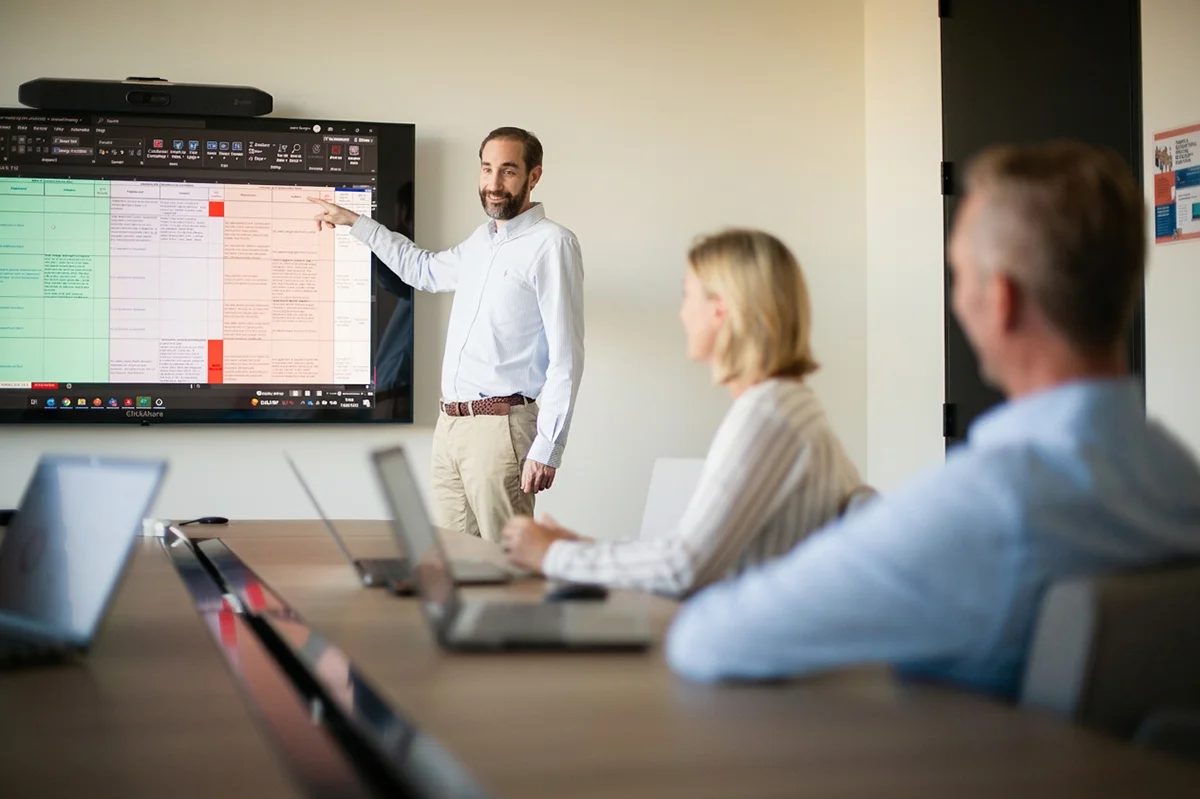
Some members of the Advisory team smiling while presenting some slides in the Kontich office.

Do you still have some questions?

Service tiers

Choose your level: Core, Foundation or Advanced

Just getting started, ready for the next step or security as a top priority? Every organisation finds a fitting entry level, extendable with extra modules such as pentesting, AD assessments and awareness programmes.

Core: We map your current posture

For SMEs in the discovery phase or a new C-level getting up to speed. A high-level reality check without detail overload, and arguments to convince the board.

Foundation: We assess your posture in depth

For organisations with the basics in place, often after feeling the impact of an attack. An in-depth check with actionable steps and a clear view on where to invest first.

Advanced: We assess and build your roadmap

For organisations with a compliance obligation ahead. Adds the business view: crown jewels, risk register and a 2-3 year roadmap towards compliance.

Contact

Tell us where you stand today.

FAQ

Everything you still wanted to know in one place

What happens after the maturity assessment?

Each of the ten roadmap points is a natural next step. Think of an AI-driven pentest to validate technical findings, an awareness programme or guidance on policies.

Does this maturity assessment prepare us for a CyFun verification?

Yes. We follow the CyberFundamentals Conformity Assessment Schema, so the report shows exactly what still needs to be addressed before a certificate is within reach.

Do we need to have policies or documentation already for a maturity assessment?

No. The assessment works at every maturity level. With Foundation and Advanced you also receive a recommended policy set as part of the result.

What is the difference between a maturity assessment and an audit?

An audit tests against a standard and ends in conformity or deviation.

Our assessment is collaborative, contextual and action-oriented: you get a scored view plus an executable plan.

How long does a maturity assessment take?

Core runs two to three weeks, Foundation one to two months and Advanced two to three months, depending on the availability of your stakeholders.

Which framework is the maturity assessment based on?

On the CyberFundamentals framework of the Centre for Cybersecurity Belgium (CCB). It consolidates NIST CSF, NIST SP 800-53, CIS Controls v8 and the ISO 27000 series into one holistic model, tailored to the Belgian context.

Explore our other Cyber Security Advisory Services

NIS2 Compliance

Awareness Program

AI-driven Exposure Management

ACEN logo with orange swirl
Privacy Overview

This website uses cookies so that we can provide you with the best user experience possible. Cookie information is stored in your browser and performs functions such as recognising you when you return to our website and helping our team to understand which sections of the website you find most interesting and useful.