Multi-Factor Authentication (MFA)

Passwords alone are no longer enough to protect access to business-critical systems and data. Multi-Factor Authentication adds an additional layer of verification to reduce the risk of account compromise, credential theft and unauthorized access. But effective MFA is more than simply enabling a second factor. We help organizations build an MFA strategy that protects identities consistently across cloud and on-premises environments, while keeping authentication practical for users and administrators.

From everyday workforce access to privileged accounts, remote access and legacy applications, we identify where stronger authentication is needed and implement controls based on risk, context and business impact.

Common problems
Our solutions

MFA only protects cloud applications

Many organizations have introduced MFA for Microsoft 365 and other SaaS applications, while access to on-premises systems, servers and legacy applications still relies primarily on usernames and passwords. 

Extend MFA beyond the cloud

We identify authentication paths that remain dependent on passwords and extend strong authentication to on-premises resources, privileged access and critical applications. 

The result is a more consistent identity security model across the entire environment. 

Too many MFA prompts frustrate users

Poorly designed MFA implementations can lead to excessive authentication prompts, user frustration and MFA fatigue. 

Users may eventually approve requests without properly checking them, reducing the effectiveness of the control. 

Apply MFA based on context and risk

We design authentication policies around the user, device, application, location and level of risk. 

Trusted and compliant scenarios can remain frictionless, while sensitive or unusual access requires stronger verification. 

Security increases without making every login more complicated.

Privileged accounts remain a high-value target

Administrator accounts, service administrators and other privileged identities can provide attackers with extensive access when compromised. 

A password leak or stolen session can therefore have a much larger impact than a normal user account compromise. 

Strengthen authentication for privileged access

We apply stronger authentication requirements to administrative and high-risk access paths. 

This can include phishing-resistant authentication, stronger controls for privileged sessions and additional protection for access to sensitive infrastructure. 

Legacy systems make MFA difficult

Older applications and infrastructure were often designed before modern authentication existed. 

Replacing these systems immediately is rarely realistic, which can leave important authentication paths insufficiently protected. 

Protect legacy access without waiting for replacement

We assess how users authenticate to legacy systems and determine where additional authentication controls can be introduced without redesigning the entire application. 

This allows organizations to reduce identity risk while modernisation takes place gradually.
Results

What can you expect?

Full visibility into authentication

A clear picture of how users and administrators sign in across the environment, including which sign-in paths aren't well enough protected.

A practical, risk-based MFA strategy

Covering cloud, on-premises and privileged access, with policies that respond to risk instead of prompting for MFA everywhere.

Stronger protection for high-value accounts

Extra safeguards for administrative and sensitive accounts, using phishing-resistant methods where appropriate and relying less on passwords.

A phased implementation roadmap

Rollout in stages, ordered by business priorities and how much each stage affects users.

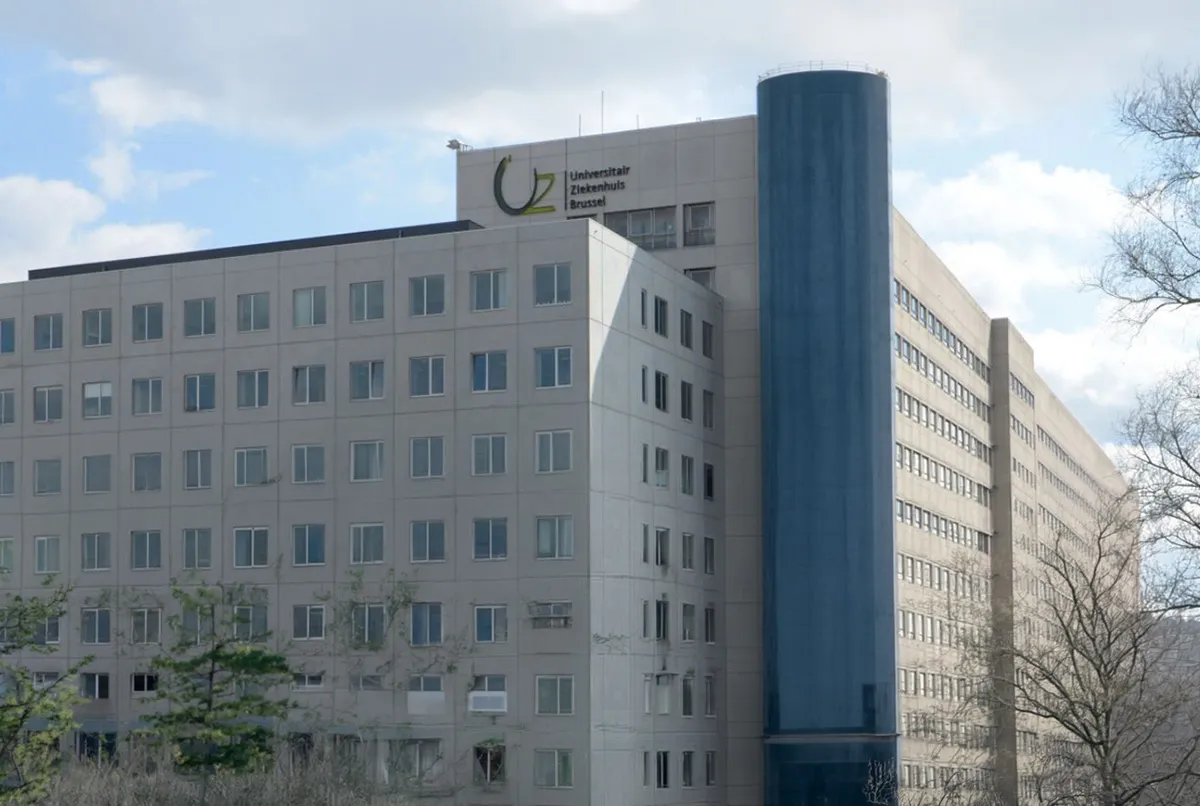
Multi-Factor Authentication. Photo of the hospital UZ Brussels, taken outside.
Reference case

The right sign-in method for every patient

Multi-Factor Authentication. Photo of the hospital UZ Brussels, taken outside.

The PrimUZ patient portal serves UZ Brussel and its partner hospitals, so it has to work for a very wide range of users.

ACEN built a secure, user-friendly login on Keycloak (open source) with several strong ways to sign in: eID, itsme, SMS or an authenticator app (TOTP).

Every patient can use a method that suits them, and other hospital applications can reuse the same central authentication.

How we approach MFA

Phase 1Discover

We map the existing authentication landscape. 

We look at users, administrators, applications, cloud services, servers, remote access and legacy systems to understand where and how authentication takes place.

Phase 2Assess

We identify authentication gaps and high-risk access paths. 

Special attention is given to privileged accounts, password-only authentication, legacy protocols, sensitive applications and systems that cannot use modern authentication. 

Phase 3Design

We create an authentication strategy based on risk. 

We define where MFA is required, which authentication methods are appropriate and where stronger phishing-resistant authentication should be introduced. 

The design takes security, usability and operational impact into account.

Phase 4Implement & Improve

We implement the authentication controls in phases, starting with the highest-risk identities and access paths. 

After deployment, policies can be continuously reviewed and improved as the environment, threats and authentication technologies evolve.

Multi-Factor Authentication. Photo of one of ACEN's Cybersecurity consultants seated behind his pc screen.

Do you still have some questions?

Privileged Access management. Some ACEn members scribbling something down, photo taken over their shoulders.
Blog article

MFA at the moments that matter most

Privileged Access management. Some ACEn members scribbling something down, photo taken over their shoulders.

Storing admin passwords in a vault is no longer enough.

This post explains why organisations are moving to Zero Standing Privileges: no default admin rights, temporary access for specific tasks, and multi-factor authentication at every critical action, not just at login.

Contact

Ready to strengthen authentication across your environment?

Whether you are introducing MFA for the first time, improving an existing implementation or extending strong authentication to on-premises systems, we can help you define and implement the right approach.

Contact us to discuss your MFA strategy.  

FAQ

Everything you still wanted to know in one place

How do we know if our current MFA setup is sufficient?

We recommend reviewing more than whether MFA is technically enabled. A proper assessment should examine MFA coverage, excluded users, authentication methods, privileged accounts, legacy authentication, on-premises access and scenarios where MFA can potentially be bypassed.

The result should provide a clear view of both existing protection and remaining authentication gaps.

Where should we start with MFA?

Start by understanding your authentication landscape. Identify which users, administrators, applications and systems still rely on password-only authentication.

From there, prioritise privileged accounts and high-impact systems before expanding the approach across the broader environment.

Can MFA replace passwords?

Increasingly, yes. Modern authentication technologies such as passkeys and hardware-backed authentication allow organisations to move towards passwordless authentication.

However, most organisations will transition gradually because existing applications and infrastructure may still depend on passwords.

Does MFA create more work for users?

It can if it is implemented poorly. A good MFA strategy avoids unnecessary prompts and uses context to determine when additional authentication is required.

The objective is stronger security with as little disruption as possible.

What about applications that do not support MFA?

Legacy applications do not always need to be replaced immediately. In many situations, MFA can be introduced at another layer of the authentication process or through an identity security control in front of the application.

The appropriate approach depends on how the application authenticates users.

Can MFA protect on-premises applications?

Yes. Many organisations initially introduce MFA for cloud applications but continue to have important on-premises authentication paths.

Depending on the application and authentication method, additional controls can often be introduced to protect access to servers, applications, remote access and other on-premises resources.

What is phishing-resistant MFA?

Phishing-resistant authentication uses methods that are designed to prevent users from accidentally providing authentication information to a fraudulent website or attacker.

Examples include hardware-backed security keys, passkeys and certificate-based authentication.

These approaches provide significantly stronger protection than traditional password and approval-based authentication.

Should administrators use stronger MFA?

Yes. Privileged identities are particularly valuable to attackers and should receive stronger protection.

Organisations should consider phishing-resistant authentication methods and additional access controls for administrative accounts.

Do we need MFA for every user?

MFA should generally protect all users, but authentication requirements do not necessarily need to be identical for every situation.

The level of authentication can depend on factors such as the user, application, device, location, privilege level and risk associated with the login.

Is MFA enough to stop account compromise?

MFA significantly improves account security, but it should not be considered a complete identity security solution. Attackers can still use techniques such as phishing, session theft, MFA fatigue and attacks against legacy authentication.

Strong MFA should therefore be combined with identity monitoring, access policies, device security and secure authentication methods.

What is Multi-Factor Authentication?

Multi-Factor Authentication requires users to provide more than one form of verification before access is granted. Instead of relying only on something the user knows, such as a password, authentication can also use something the user has or something that uniquely verifies the user.

This significantly reduces the risk associated with stolen passwords.

Explore our other Identity Security Services

Endpoint Security

Identity Threat Detection and Response (ITDR)

Certificate Lifecycle Management (CLM)

Secrets Management

Identity Infrastructure Security

Workforce Access and Single Sign-On

ACEN logo with orange swirl
Privacy Overview

This website uses cookies so that we can provide you with the best user experience possible. Cookie information is stored in your browser and performs functions such as recognising you when you return to our website and helping our team to understand which sections of the website you find most interesting and useful.