Incident Response and Forensics

Think you’ve been breached? Our Incident Response & Forensics team investigates, contains, and helps you recover from cybersecurity incidents, from phishing and ransomware to full-scale data breaches.

As a partner to leading cyber insurance providers, our response and forensic investigation is backed by real-world incident expertise, built through handling a constant stream of cases across industries. 

Quickly identify, contain, and resolve incidents before they escalate into a bigger problem.

Get uninterrupted access to our Incident Response team, without vetting delays.

As a partner to leading cyber insurance providers, our response and documentation are shaped by real world incident expertise, built through a constant flow of cases across the industry.

Common problems
Our solutions

You suspect a breach and don't know how bad it is.

Without immediate expert support, it's unclear how far an attacker has moved, what's been affected, and what to do first. Every hour of uncertainty increases the damage.

Our Incident Response & Forensics team assesses scope and impact fast.

We investigate from the first call, determining what happened, how far it spread, and what needs to happen next, so decisions are based on evidence, not guesswork. 

There is no clear definition of roles and responsibilities.

During an incident, people don't know who makes decisions, who communicates, or who performs the technical response. Organizations struggle to maintain critical services while responding to an incident.

Ownership and accountability are assigned from the outset.

Define, document, and communicate Incident Response roles and responsibilities. This ensures stakeholders understand their responsibilities and enables a coordinated response to cybersecurity incidents. 

Slow detection and escalation and poor communication heighten risk.

Incidents are often detected too late or escalated too slowly. During a crisis the real challenge becomes getting IT, management, legal, and business teams aligned, aside from responding to the crisis at hand. 

Clear escalation paths and stakeholder communication are established.

This ensures incidents are managed consistently. Decision makers are engaged at the right time. And response efforts remain coordinated throughout the incident lifecycle. 

Resources and skills are limited in time and cost.

There is a lack of executive buy-in resulting in constrained budgets and limited expertise. IR is often viewed as an IT issue rather than a business resilience requirement. 

Predictable investments support budget planning.

Leadership provides strategic direction, governance, and support for Incident Response initiatives, ensuring the necessary capabilities, resources, and expertise are in place.

Your insurer requires proof of what happened before they'll pay out.

Cyber insurance claims are often delayed or denied without proper documentation of the incident, its cause, and the response taken. 

As a partner to leading cyber insurance providers, our investigation is built for your claim.

Our forensic investigation and reporting are aligned with what insurers expect, helping your claim move faster and reducing the risk of disputes.
Results

What can you expect?

Emergency Incident Response
Experienced responders, backed by a constant flow of real incidents
Forensic investigation with clear documentation
Coordination and management throughout the incident
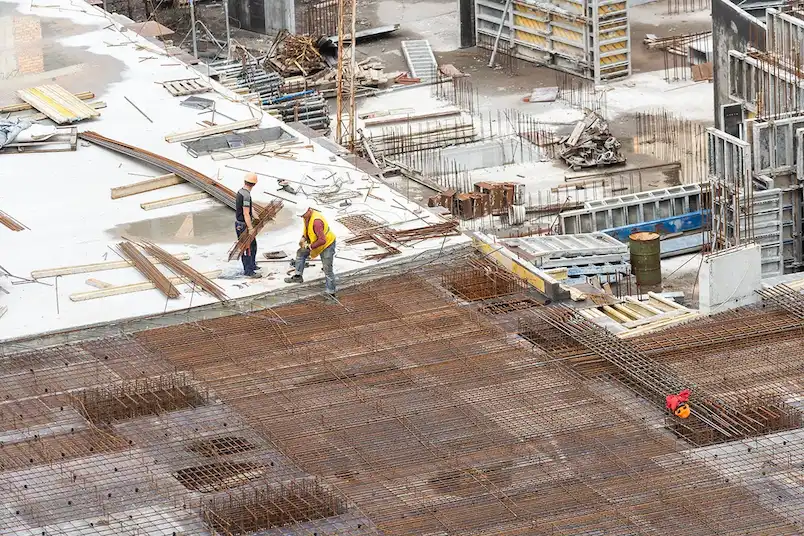
Incident Response and Forensics. External Attack Surface Management. Image of a construction site with some workers carrying steel bars.
Reference case

Incident-ready across 100 construction sites

Incident Response and Forensics. External Attack Surface Management. Image of a construction site with some workers carrying steel bars.

Willemen Groep chose to stop reacting to incidents and start preparing for them.

Without central visibility, they couldn’t easily tell where an incident might start, how far it could spread, or who should respond. As a result, any incident would be slower to contain and harder to investigate.

How we’re stopping attacks in their tracks

Detect Identify a suspected cybersecurity incident

Suspicious emails, unauthorized access attempts, malware alerts, or unexpected system behaviour could be early indicators. What was observed, when, and which users or systems may be affected? 

Report Report the incident through the designated channel

Provide all available information, including any actions already taken. Timely and accurate reporting helps proper assessment and prioritization and supports effective decision-making.

Contact Contact Incident Response

Engage the Incident Response team or service provider according to the established escalation process. Early engagement helps mobilize the right expertise quickly and minimize business disruption. 

Coordinate Coordinate the response

Maintain consistent communication with the Incident Response team, management, legal, communications, and other key stakeholders throughout the incident. It keeps response efforts aligned and helps ensure regulatory, contractual, and organizational obligations are addressed appropriately. 

Incident Response and Forensics. One of Acens female SOC Engineers at work behind his screen in the Security operations Center.

Do you still have some questions?

Components

What makes up our Incident Response and Forensics service

When a breach hits, every second counts. We contain the damage, investigate what happened and guide you through recovery, from the first call to the final report.

Incident Response Retainer (IRR)

Have our experts ready to deploy the moment an incident occurs. Pre-defined SLAs guarantee fast response times, while a proven response plan helps minimize damage and recovery time when every second counts.

Forensic Investigation

Following an incident, our experts investigate root cause, scope, and impact, producing clear documentation of exactly what happened, how the attacker got in, what was affected, and what was done to contain and remediate it.

Coordination

Throughout an incident, we maintain consistent communication with your Incident Response team, management, legal, communications, and other key stakeholders. This keeps response efforts aligned and ensures regulatory, contractual, and organizational obligations are addressed appropriately.

Insurance Partnerships

ACEN is partnered with leading cyber insurance providers. Our incident response and forensic investigation processes are aligned with what insurers expect, helping your claim move faster and keeping your coverage intact.

Contact

Call us before you need us. Our experts are here to help you.

FAQ

Everything you still wanted to know in one place

How does the forensic research work in detail?

The affected users, endpoints, servers, applications and data are identified through analysis of available evidence and telemetry. This helps determine the extent of the compromise and guides response priorities.

The incident is investigated to determine how the attacker gained access, what actions were performed and which vulnerabilities or weaknesses were exploited. Identifying the root cause is essential to preventing recurrence.

What happens if there's sensitive data involved during an incident?

Our experts assess the type and volume of data affected, determine potential business impact and support any required notification or reporting activities.

Containment and recovery efforts are prioritised based on the risk to the organisation.

Is there an incident reporting obligation in Belgium?

Yes. Organisations subject to NIS2 must report significant cybersecurity incidents to the Centre for Cybersecurity Belgium (CCB) within the prescribed deadlines.

If personal data is involved, notification to the Belgian Data Protection Authority (GBA) may also be required. Our experts assist with these reporting requirements and the full notification process.

Should we pay the ransom when we are breached?

No, there is no guarantee that attackers will provide a working decryption key, return stolen data or refrain from future attacks.

Paying may also encourage further criminal activity and can create legal, regulatory or insurance complications.

Explore our other Detection and Response Services

Vulnerability Management

Managed Detection and Response (MDR)

External Attack Surface Management

ACEN logo with orange swirl
Privacy Overview

This website uses cookies so that we can provide you with the best user experience possible. Cookie information is stored in your browser and performs functions such as recognising you when you return to our website and helping our team to understand which sections of the website you find most interesting and useful.