Managed Detection and Response (MDR)

With ACEN’s Managed Detection and Response, you receive the support and decisiveness of a fully operational, local Security Operations Center (SOC). A dedicated team of cybersecurity experts monitors, detects, and responds to threats 24/7, acting as a true extension of your in-house security team. 

Spanning the entire IT infrastructure, our CSIRT (Computer Security Incident Response Team) detects, prevents and responds to threats proactively and in real-time. 

Our SOC, the engine behind MDR, operates as a 24/7 command center. A team of security professionals and carefully selected tools and processes monitors, analyzes and improves security postures continuously. 

Common problems
Our solutions

Too many notifications creating alert fatigue.

Critical threats get overlooked. Indicators that go unnoticed may develop into security incidents that could have been identified and prevented.

Automated filtering and prioritization set a clear, focused set of actions.

Smart alert filtering significantly reduces the number of notifications. This ensures critical alerts are prioritized, investigated, and remediated accordingly. 

AI entities move faster than human operators.

AI created a new attack surface. Agents operate autonomously and at machine speed, not having to comply with traditional controls and company policies. They create an entirely new challenge in governance.

Pattern recognition and AI-integration allow strategic, proactive targeting.

Our SOC uses AI tooling to help increase productivity, speed and efficiency in forecasting and detecting risks. AI predicts, our experts act. Together, they deliver real stopping power against threats.

Limited budget and time increases pressure on internal teams.

Daily operational demands and constrained cybersecurity budgets limit the ability of internal IT teams to build specialized expertise and keep a proactive security posture. 

Fixed prices and SLAs provide budget insight and operational efficiency.

A fixed per-user pricing model ensures budget predictability. Security investments become easier to justify and measure against ROI, proving their worth.

There is a lack of dedicated security experts.

IT teams consist of generalists, lacking expertise and experience in cybersecurity best practices, industry standards, and modern security frameworks.

Expert human analysts bring years of experience and deep expertise.

Our robust threat intelligence capabilities ensure we're keeping up with attack methodologies and indicators. Extend your team with experts, who understand your unique challenges and goals.
Results

What can you expect?

A scalable SOC solution that evolves with your organization
Weekly reports that allow auditing and compliance assessments
A roadmap ranking priorities and addressing quick wins
Seamless integration with any environment, operating under 1 shared context
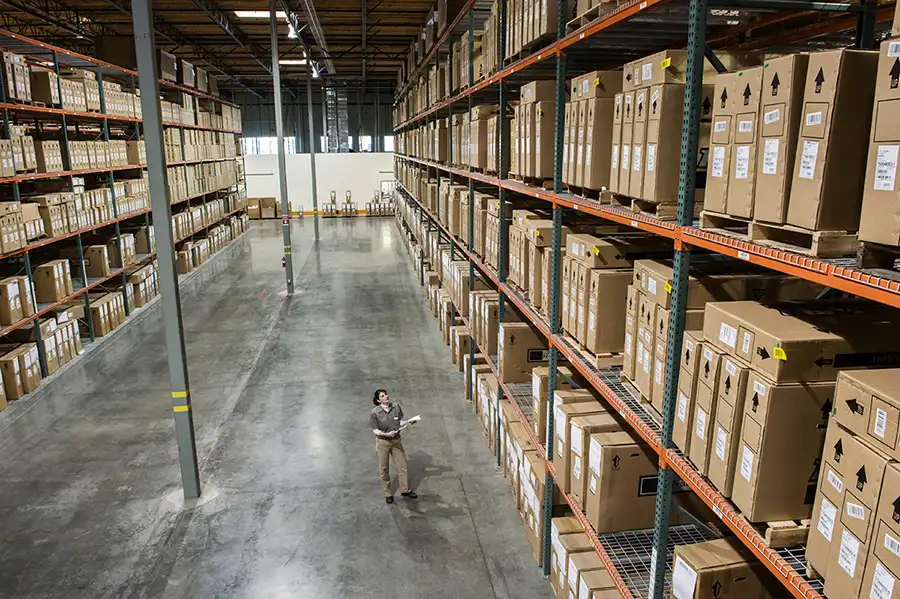
Image of a big warehouse, taken from aboven showing someone walking around.
Reference case

How we implemented a full SOC at A&C Systems

Image of a big warehouse, taken from aboven showing someone walking around.

A&C Systems, headquartered in Belgium, is a leading wholesale and service partner in the consumer electronics industry. Handling sensitive customer data and proprietary information every day, the company needed stronger digital defences against evolving threats.

The main challenge: refining its security monitoring to detect cyberthreats effectively.

How our SOC is stopping attacks

Phase 1 Prevention & Pattern recognition

A range of security protocols and detection capabilities helps stop breaches before they escalate. Correlating Active Directory, OS, and endpoint logs enables the detection of persistence techniques and attacker behaviours. 

Phase 2 Detection & Analysis

Through combined telemetry from Identity Threat Detection and Response (ITDR), Endpoint and Extended Detection and Response (EDR and XDR), a cloud-native SecOps and SIEM platform, Vulnerability Management, and Microsoft 365 Security, our 24/7 operated Security Center can offer detection across the modern, multi-layered client environment.

Phase 3 Response and Containment

Our local SOC and dedicated CSIRT are fully based in Belgium. Through advanced security automation and proven incident response procedures, our experts can respond to threats immediately. Breaches are flagged immediately and get contained within minutes. This limits attackers’ movement through your organization, minimizes operational disturbance and lowers recovery time and budget.

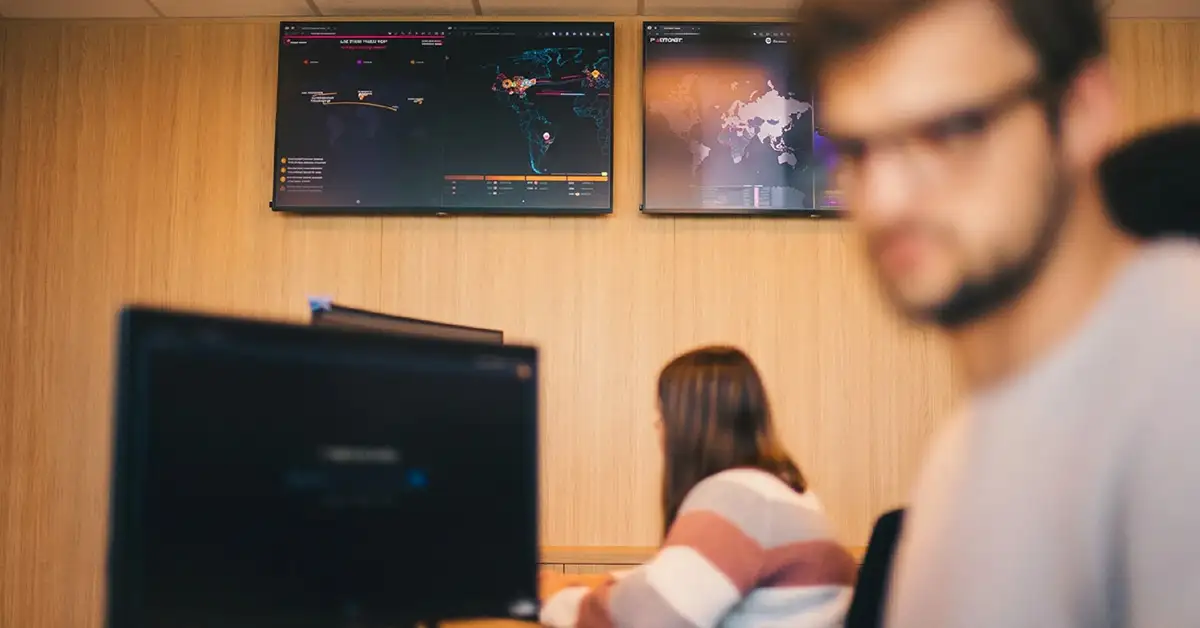
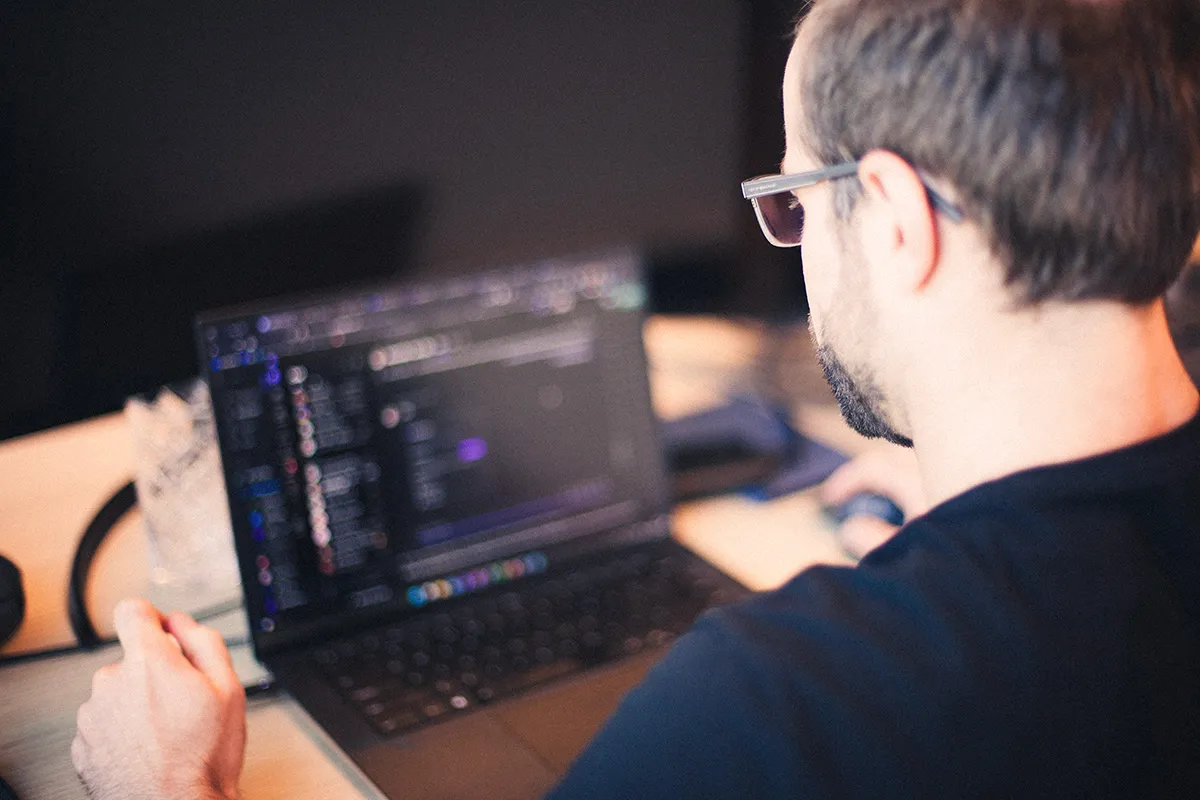
One of Acens SOC Engineers at work behind his screen in the Security operations Center.

Do you still have some questions?

Service tiers

Our service in the flavour you need

Incident Response Retainer

ACEN Incident Response Retainer gives your organization direct access to our cyber incident response experts whenever you need them. Through guaranteed CSIRT availability, pre-purchased service credits and proactive readiness activities, you can respond faster to security incidents while improving your overall resilience before an attack occurs.

24/7 access to our CSIRT team during security incidents
Service credits available for incident response and forensic investigations
On-demand threat hunting to proactively identify hidden threats
Incident Readiness Assessment to validate preparedness and response capabilities
Faster response times and expert support when every minute matters

SOC Essentials

24/7 Security Operations Center service with a focused monitoring scope, providing the perfect balance between detection capabilities and cost. We continuously monitor your environment, delivering expert analysis, alert triage, and access to our CSIRT team when incidents require escalation.

24/7 monitoring across key log sources
Expert alert triage and threat validation
Access to our CSIRT for incident guidance and escalation support
Monthly reporting and actionable security recommendations
Cost-effective protection with a clearly defined monitoring scope

Full SOC

24/7 security monitoring across all security-relevant log sources within your environment. Acting as an extension of your security team, our analysts continuously detect, investigate and respond to threats while helping strengthen your overall security posture through proactive threat hunting and expert guidance.

24/7 monitoring across all security-relevant log sources
Advanced threat detection, investigation and analyst-led triage
Rapid incident response and containment support
Proactive threat hunting and continuous security improvement
Strategic security guidance and executive reporting

The SOC engineers at work in their private Security operations Center in the ACEN Kontich office.
Blog article

ACEN MDR expands Silverfort integration for Identity Security

The SOC engineers at work in their private Security operations Center in the ACEN Kontich office.

83% of organisations have suffered a breach through compromised credentials (Osterman Research). Yet Silverfort, built to stop exactly that, often runs at a fraction of its potential. Without dedicated upkeep, policies go stale and coverage drifts.

ACEN fixes that: our Silverfort specialists keep the platform sharp, and our 24/7 SOC acts on what it sees.

Contact

There's a SOC solution for every need.

FAQ

Everything you still wanted to know in one place

Explore our other Detection and Response Services

Vulnerability Management

Incident Response and Forensics

External Attack Surface Management

ACEN logo with orange swirl
Privacy Overview

This website uses cookies so that we can provide you with the best user experience possible. Cookie information is stored in your browser and performs functions such as recognising you when you return to our website and helping our team to understand which sections of the website you find most interesting and useful.