Vulnerability Management

Vulnerability Management is about assessing, prioritizing, and remediating security weaknesses across an organization’s IT environment. 

From operating systems and applications to cloud services and network devices, vulnerabilities create opportunities for attackers if left unaddressed.

Common problems
Our solutions

Data overload and alert fatigue create hidden risks.

Vulnerability data without sufficient context creates noise. Security teams are overwhelmed by long lists of findings and struggle to distinguish critical risks from lower-priority issues. As a result, important vulnerabilities may be overlooked, leading to reactive, audit-driven remediation and alert fatigue.

Exposure management turns vulnerabilities into actionable priorities.

Combining threat intelligence, exploitability, asset criticality, and attack path analysis allows organizations to focus remediation efforts on the vulnerabilities most likely to impact critical infrastructures. Aligning business and IT enables a structured approach under shared context, and clear responsibilities.

Patching, misconfiguration and siloed tools cause drift and disconnect.

Misconfigurations, configuration drift, and delayed patching can create significant security risks over time. Combined with legacy systems that cannot be easily upgraded and disconnected security workflows, organizations struggle to manage exposures.

Gain a clearer insight and better predict impact & risk.

Combining AI, threat intelligence, and continuous scanning provides clear visibility into vulnerabilities, misconfigurations, and their potential business impact. Define exposure policies, strengthen security hygiene, and prioritize remediation based on risk. This allows reduced exposure and improved governance. 
Results

What can you expect?

Vulnerability Assessment
Risk Prioritization
Guided Remediation
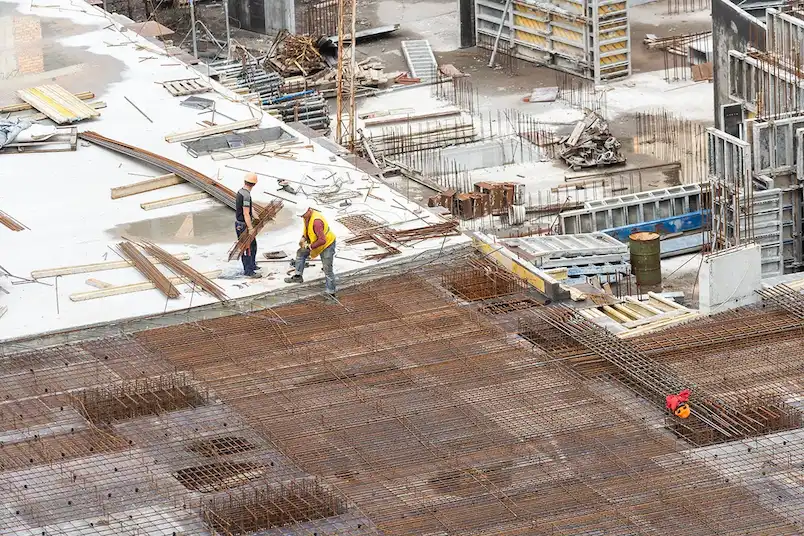
Incident Response and Forensics. External Attack Surface Management. Image of a construction site with some workers carrying steel bars.
Reference case

Clear vulnerability insight across 100 construction sites

Incident Response and Forensics. External Attack Surface Management. Image of a construction site with some workers carrying steel bars.

With 100 active construction sites and many temporary joint ventures, Willemen Groep runs a large and constantly changing environment.

To stay ahead in that environment, they needed central visibility. That would let them spot vulnerabilities early and decide which ones to fix first.

How Vulnerability Management impacts your environment

Phase 1 Assess

Identify vulnerabilities, misconfigurations, exposed services, and missing security controls through continuous scanning and configuration assessments. Enrich findings with Common Vulnerability Scoring System (CVSS), threat intelligence, and exploitability data. 

Phase 2 Prioritize

Correlate metrics. Focus remediation efforts on exploitable vulnerabilities that present the highest operational or business risk.  

Phase 3 Remediate

Reduce exposure through patch deployment, configuration hardening, compensating controls, network segmentation, or risk acceptance. Align expectations through defined ownership and response times. 

Phase 4 Measure

Track exposure reduction, remediation performance, and overall cyber risk over time. Dashboards and reporting drive governance and continuous improvement. 

Vulnerability Management. One of Acens SOC Engineers at work behind his screen in the Security operations Center.

Do you still have some questions?

Vulnerability Management. Image of one of ACENs engineers looking at his screen, photo taken over his shoulder with his screen blurred.
Blog article

How Mythos will impact threat intelligence

Vulnerability Management. Image of one of ACENs engineers looking at his screen, photo taken over his shoulder with his screen blurred.

Mythos vulnerability assessment: Friend or foe? It has been a popular topic for the past months. The debate continues, but its impact is undeniable.

By uncovering hidden assets, exposures, and potential attack paths, Mythos is reshaping how organizations understand and manage cyber risk.

Contact

Let's not meet by accident.

FAQ

Everything you still wanted to know in one place

What if a vulnerability cannot be patched?

Some legacy systems, proprietary applications and specialised hardware cannot be upgraded due to operational, compatibility or vendor constraints. In these cases, the focus shifts from patching to reducing exposure and managing risk.

Organisations must identify affected assets, assess their criticality and monitor for signs of exploitation. Compensating controls such as network segmentation, restricted access, system hardening, intrusion monitoring and enhanced detection capabilities help limit attack paths and reduce the potential impact of exploitation.

What is the best approach to managing zero-day exposures?

Effective zero-day management depends on asset visibility. Security teams must quickly identify affected systems, understand their exposure and determine exploitability.

Where patching is not yet possible, compensating controls such as segmentation, EDR detection rules, WAF protections and service restrictions help reduce the attack surface until remediation is available.

What is the difference between Urgent, Critical, High, Medium, and Low vulnerabilities?

Severity levels indicate the potential impact of a vulnerability:

  • Low: low-risk information exposure
  • Medium: risk of exposing exploitable information
  • High: potential sensitive data exposure or service disruption
  • Critical: risk of system compromise or significant data exposure
  • Urgent: attackers can gain full system control

Prioritise based on risk, not severity alone.

Do I need Vulnerability Management or Penetration Testing?

Vulnerability management and penetration testing work best together. One continuously monitors security weaknesses, while the other validates how those weaknesses could be exploited.

They combine risk visibility with effective security validation.

How do CVE and CVSS work and what can I learn from them?

CVE (Common Vulnerabilities and Exposures) and CVSS (Common Vulnerability Scoring System) provide standardised information about security vulnerabilities.

You can think of a CVE as the ticket number of a vulnerability. CVSS is a framework for measuring how severe a vulnerability is. Together, they give insight into its nature and severity, and support prioritisation and the right remediation actions.

How do vulnerability management and vulnerability assessment compare?

Vulnerability assessments provide a snapshot of security weaknesses across an environment.

Vulnerability management continuously prioritises, remediates and monitors vulnerabilities based on risk and business impact over time.

Explore our other Detection and Response Services

Incident Response and Forensics

Managed Detection and Response (MDR)

External Attack Surface Management

ACEN logo with orange swirl
Privacy Overview

This website uses cookies so that we can provide you with the best user experience possible. Cookie information is stored in your browser and performs functions such as recognising you when you return to our website and helping our team to understand which sections of the website you find most interesting and useful.